Attestable Builds provide verifiable source-to-binary provenance using hardware-secured build environments.
Prove every build: hardware-signed evidence that a binary was built from its source. Know your build wasn't tampered with before you ship, not after an incident.
Step 1: Your existing build
Step 2: Runs in a hardware enclave
- Your build, unchanged
- Isolated from the host and its admins
- On AMD SEV-SNP hardware
Step 3: The chip signs what was built
Step 4: Anyone can verify it
Prove and verify how binaries are built.
When you ship a release or install a pre-compiled dependency there is usually no way to tell whether the binary really came from the source code it claims. Attestable Builds closes that gap: your existing build runs unchanged inside a hardware-protected environment, and you get a hardware-backed certificate that this exact binary was produced from this exact source. No reproducible-builds engineering, and instead of trusting the build machine or us, you check a report that chains back to the CPU vendor.
Build provenance is becoming standard: GitHub can attest your CI runs, and Google's OSS Rebuild covers popular npm and PyPI packages. But those proofs ask you to trust the platform that issued them; ours are rooted in CPU hardware you can check independently. And some ecosystems have no provenance at all: For example, Maven Central ships pre-compiled .jar files without provenance information. There, we rebuild the package from its published source in an attested environment and certify whether it matches the binary on the registry.
Early Access: try it yourself
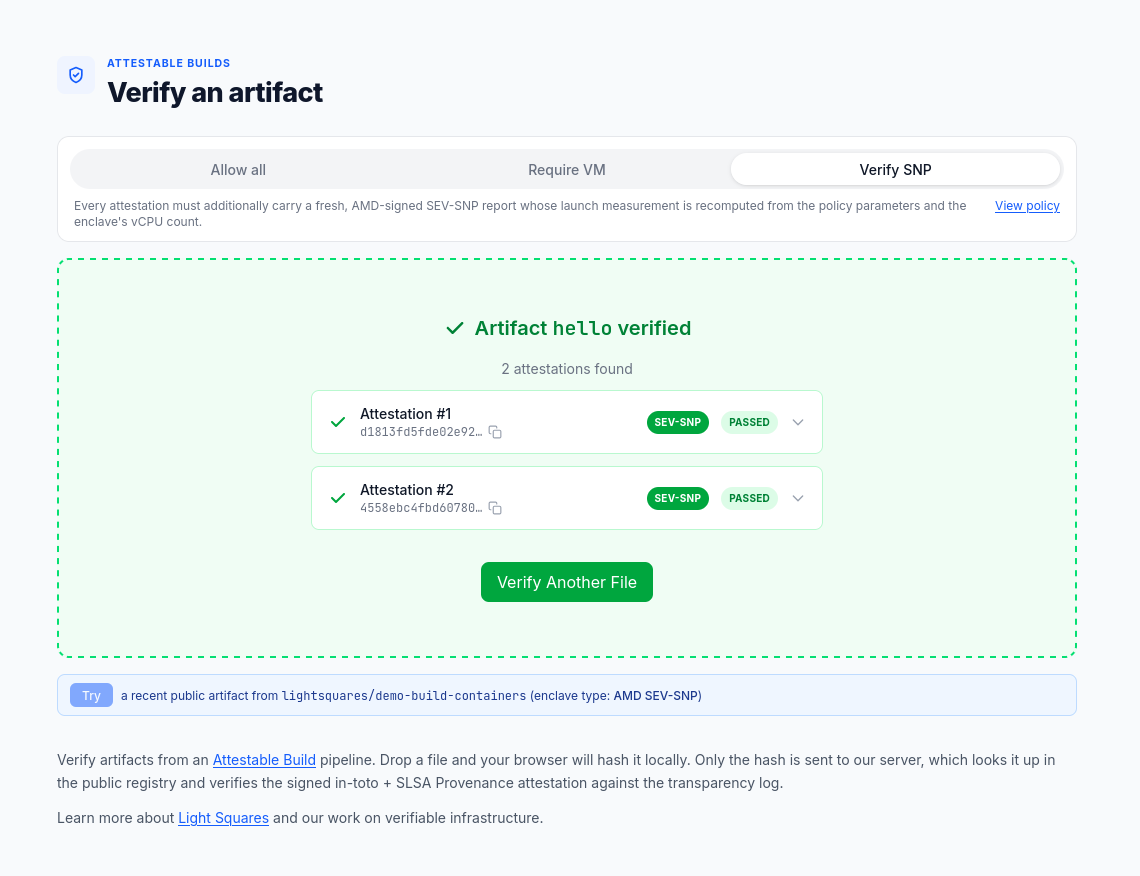
Attestable Builds runs on our platform today. Drop any artifact at app.lightsquares.dev/verify and your browser checks its signed in-toto + SLSA provenance attestation against the transparency log, including the AMD-signed SEV-SNP report. A public demo artifact is already available; running your own builds is currently invite-only. How to read the result →
Want attested builds for your own project?
Our skill sets it up with your coding agent.
Add Attestable Builds to this project using the skill at https://github.com/lightsquares/skills/blob/main/lightsquares-attestable-builds/SKILL.md- Provenance Where It's Missing
- Pre-compiled ecosystems like Maven ship binaries that are hard to trace back to their source. We enable building them from their published source in an attested environment and certify the match.
- Hardware-based Trust
- Use hardware-backed security to protect build integrity without trusting the infrastructure provider. Ready for SLSA Build L3, with hardware isolation guarantees that go beyond what L3 requires.
- Attests the Audit PipelineComing
- The same attested-execution machinery will run under Dependency Canary, proving the audit process itself ran untampered.
- Seamless CI/CD Integration
- Integrate with existing workflows (e.g., GitHub Actions, GitLab) with minimal changes and benefit right away from strong, verifiable build guarantees.
Attestable Builds vs Reproducible Builds
Reproducible Builds make a build bit-for-bit deterministic, so anyone can rebuild the source and compare the result. That is a powerful guarantee, but it takes significant engineering and ongoing upkeep, and someone still has to actually do the rebuilds. Attestable Builds takes a different route: the hardware proves that each individual build ran untampered, with no determinism work required. The two approaches are complementary, and both beat taking a binary on trust.
What this means for your team
CISO
- Replace blind trust with verifiable provenance for the artifacts you ship.
- Mitigate insider threats and reduce the trust placed in build infrastructure.
- Make audits easier, both for your own organization and for the suppliers you depend on.
DevOps
- Integrates with GitHub Actions and other git-based repositories, without replacing your existing pipeline.
- Avoid the engineering effort of Reproducible Builds.
Software Engineer
- Skip the upfront engineering effort of making builds deterministic.
- Apply dependency and security updates without breaking build verifiability.
- Keep standard Docker-based builds; they run unchanged inside the attested environment.
Get ahead of your supply chain.
Talk to the founders or request early access to run your own attested builds.